
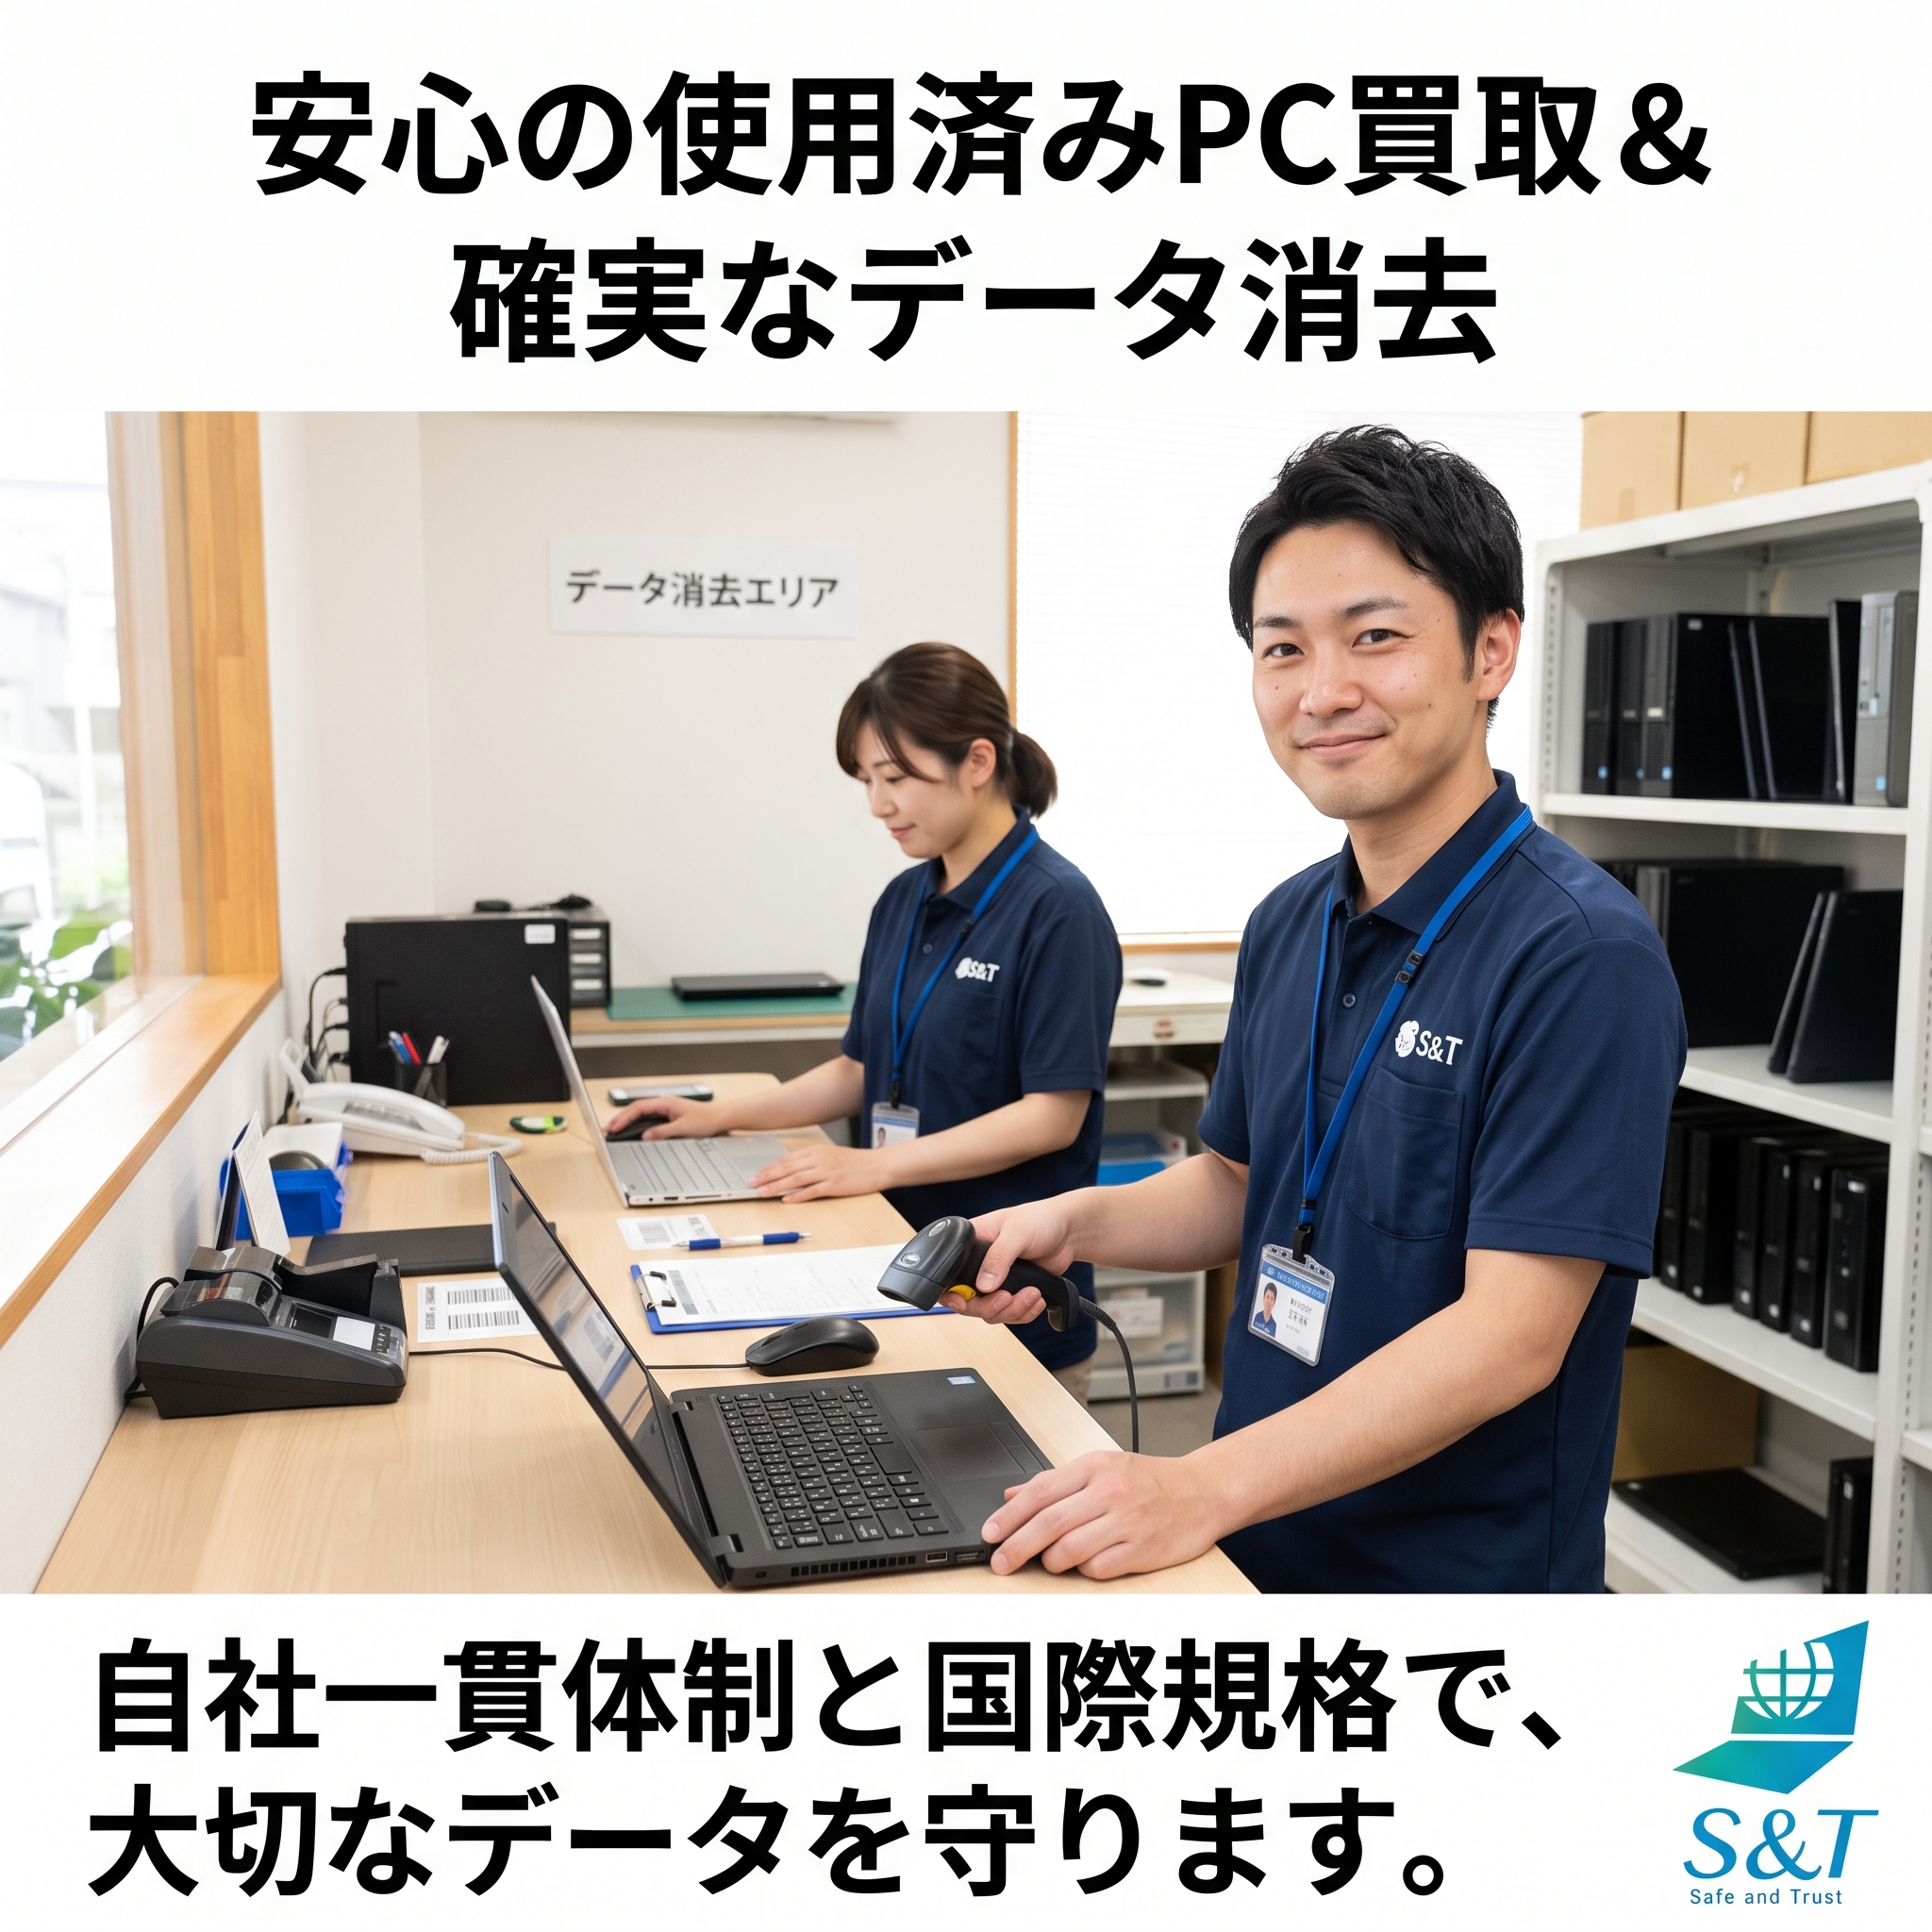
連日のようにニュースを賑わせるサイバー攻撃やランサムウェアの被害。標的型メールへの対策、UTM(統合脅威管理)の導入、従業員へのセキュリティ教育など、入口の防御に注力されている情報システム部門や総務・経営企画の担当者様も多いのではないでしょうか。
しかし、企業のセキュリティ対策において意外な落とし穴となっているのが「社内IT資産の出口(売却・入替)」です。
定期的なPCの一斉更新で不要になった端末、事業拡大やテレワーク環境の見直しに伴って余剰となったノートPC、倉庫やオフィスの片隅に保管されたままの自社所有デスクトップPC。それらを「手放す瞬間」のセキュリティ対策は万全でしょうか。
「OSの初期化(フォーマット)をかけたから大丈夫」 「リサイクル業者にまとめて引き渡したから問題ないだろう」
もしそうお考えなら、重大な情報漏えいリスクを抱えているかもしれません。
今回は、法人向け自社所有PC買取・リユース・データ消去を手がけるS&T株式会社が、なぜそこまで徹底して「確実な消去」と「トレーサビリティ(追跡性)」にこだわるのか、現場のリアルな運用とともにお伝えします。
1. 巧妙化するサイバー攻撃の裏で潜む「物理的漏えい」の死角
企業がサイバー攻撃を受けると、顧客データ、取引先の機密情報、従業員の個人情報、知的財産などが瞬時に外部へ流出します。社会的信用の失墜、巨額の損害賠償、事業停止など、その打撃は計り知れません。
しかし、データの流出経路はネットワーク経由だけとは限りません。近年、世界中で問題視されているのが「使用済みストレージの不完全な消去による物理的漏えい」です。
「ごみ箱を空にする」「クイックフォーマット」は消去ではない
OS標準の「フォーマット」や「初期化」を実行しても、実はデータそのものが消えたわけではありません。本に例えるなら「目次」を消しただけで、本文(データ実体)はストレージ内部にそのまま残っています。市販の復元ソフトや無料ツールを使うだけで、削除したはずの見積書、契約書、メール履歴、顧客台帳が簡単に復元できてしまうケースが多々あります。
社外に出た瞬間、誰がどう扱っているのか?
引き取りを依頼した業者がさらに別の下請け業者へ転送し、途中の運送過程や保管倉庫で紛失・盗難・抜き取りが発生する事例は後を絶ちません。どれほど頑丈なファイアウォールを社内ネットワークに張っていても、使い終わったPCがたった1台流出するだけで、企業のセキュリティ体制は根底から崩壊します。
自社資産であるPCの更新・売却は、単なる「不要品の片付け」ではなく「最高レベルの機密情報破棄オペレーション」として捉える必要があります。
2. 国際基準に準拠した上書き消去と、再起不能にする物理破壊
S&Tでは、お客様からお買い取りしたすべての端末に対し、業界最高峰のセキュリティ基準を適用しています。
国際規格に則した「ADパラレル消去(Advance社ライセンス)」の採用
データ消去ソフトウェアには、世界的な消去規格(NIST SP 800-88、DoD 5220.22-Mなど)に完全準拠したAdvance(アドバンス)社の正規ライセンスを採用しています。
この消去技術では、ストレージの全セクタに対して無意味なデータを複数回上書きし、専用の復元装置や高度な解析ツールを用いても元のデータを復元できない状態にします。SSD特有のウェアレベリング領域や代替セクタまで確実に処理するため、最新のNVMe SSD搭載PCでも安心して手放していただけます。
作業完了時には、機器のシリアル番号と紐付いた正規の「データ消去証明書」を発行いたします。社内監査やセキュリティ監査、コンプライアンス報告資料としてそのままご利用いただけます。
不良ドライブ・認識不能な端末は「穿孔物理破壊」で完全粉砕
通電しないPC、認識エラーを起こすHDD/SSD、基板故障の端末など、ソフトウェアによる上書き消去が実行できない個体も一定数存在します。
こうした端末を「壊れているから読めないだろう」と放置することは絶対にありません。S&Tでは専用のハードディスククラッシャーを用いて、記録プラッタ(磁気ディスク面)やメモリーチップを物理的に貫通・破壊(穿孔処理)します。物理的に記録面をクラッシュさせるため、外部の研究機関や復旧業者であっても復元は技術的に不可能です。ご要望に応じて、穿孔破壊後の写真付き作業報告書も提出いたします。
3. 「自分ごとのリスク」として向き合う理由
なぜS&Tは、ここまで厳格にデータ消去を徹底するのでしょうか。
それは、私たちが単なる「中間ブローカー」ではなく、買い取った端末の価値を再生し、自らの責任でリユース市場へ送り出す当事者だからです。
リユースPCとして次のユーザーへ端末をお届けする際、もし万が一にも前の持ち主様のデータが1バイトでも残っていれば、被害を受けるのはお客様だけではありません。S&Tという会社の信用も一瞬で失墜します。
「お客様のリスクは、私たちのリスクそのものである」
この当事者意識があるからこそ、私たちは消去作業を決してルーティンワークとして流しません。1台1台のストレージに対し、自社の存亡がかかっているという強い緊張感を持って向き合っています。
「機械が勝手にやってくれる」と過信せず、消去ログのエラーチェック、消去完了ステータスのベリファイ(検証)、作業ログの突合まで、人の目とシステムの両軸で二重三重の確認を行っています。
4. 外部委託ゼロ。自社便引取とバーコード個体管理がもたらす安心感
どれほど消去技術が優れていても、引き取りから作業までの過程に隙間があればセキュリティは成立しません。S&Tのオペレーションは、透明性と追跡性を最優先に設計されています。
① バーコードによる全数個体管理
回収した機器は、入荷した瞬間に固有の管理バーコードを貼付し、シリアル番号、メーカー、モデル、搭載ストレージの型番を一元管理します。 「今、どのPCがどの工程(検品/消去中/物理破壊/完了)にあるのか」が明確に追跡できるため、ロット内での混同や作業漏れ、紛失を構造的に防ぎます。
② 自社便での引き取り対応
大手の運送会社に混載便で依頼すると、積み替え拠点での紛失リスクや手荒な荷扱いによる破損リスクが付きまといます。S&Tでは、お客様のオフィスまで自社スタッフが直接伺い、自社便にて搬出・輸送を行います。搬出から運搬、自社作業場への搬入まで、第三者の手を一切介さないクローズドなルートを維持します。
③ 自社内での一貫作業
買い取った端末を別の処理業者へ丸投げ(横流し)することは一切ありません。すべての検品、ソフトウェア消去、穿孔物理破壊、リユース化に向けたクリーニングまで、責任を持って自社の管理下で完結させています。
5. コスト削減とセキュリティ担保を両立したい企業様へ
「セキュリティを厳格にしようとすると、廃棄費用がかさむ」 「PCを買取に出したいが、情シスのリソースが足りず社内でのデータ消去が追いつかない」
このようなお悩みを抱える企業様こそ、ぜひ一度S&Tにご相談ください。
通常、廃棄処理業者に依頼すると「データ消去費用」「運搬費用」「マニフェスト発行費用」など多くのコストが発生します。一方、S&Tはリユースを前提とした買取スキームを構築しているため、万全のデータ消去と証明書発行を担保しながら、自社保有機器の残存価値を適正に査定し、売却益の創出(IT投資コストの回収)を実現します。
社内で何日もかけて消去ソフトを回す必要はありません。PCをそのままの状態で私たちにお渡しいただければ、安全な搬出から完全消去、資産化までワンストップでサポートいたします。 ※なお、弊社でお取り扱いできるのは企業様が自社で所有(資産計上)されているPCとなります(リース品・レンタル品などの賃貸借物件は対象外となります)。
まずはご相談・無料お見積もりから
オフィスの移転、社内PCの一斉リプレイス、少数の余剰資産の整理など、台数の多寡を問わず柔軟に対応しております。
「自社のセキュリティポリシーに合う消去方法を相談したい」 「社内に眠っているPCの買取概算を知りたい」
そのようなご相談も大歓迎です。大切な企業の重要データを守り、安心して次のIT投資へ進むためのパートナーとして、S&Tをぜひご活用ください。
Cyberattacks and ransomware incidents dominate business headlines daily. Corporate IT departments, general affairs teams, and executive management continue to invest heavily in perimeter defenses—from anti-phishing training to unified threat management (UTM) gateways.
Yet in enterprise security, one glaring blind spot persists: the exit strategy for retired IT assets.
What happens to company-owned PCs replaced during tech refreshes, idle laptops left over from remote work reorganizations, or legacy desktop workstations sitting in storage? When it is time to part with these machines, are your data sanitization protocols truly foolproof?
“We already ran a factory reset.”
“We handed them over to a standard recycling vendor, so it should be fine.”
Relying on these assumptions exposes organizations to catastrophic compliance and data breach vulnerabilities.
Below is an inside look at how S&T Inc. handles enterprise PC procurement, refurbishment, and data sanitization—and why our end-to-end traceability and certified destruction standards eliminate physical data leak risks.
1. The Physical Vulnerability Lurking Behind Cyber Threats
When digital perimeters fail, customer databases, confidential contracts, employee records, and proprietary IP leak instantly—triggering reputational ruin, regulatory penalties, and operational shutdown.
However, data leakage is not confined to internet-borne attacks. A critical threat facing enterprises worldwide is physical data exposure resulting from incomplete media sanitization.
“Emptying the Recycle Bin” or “Quick Format” Does Not Erase Data
Standard operating system formats or initializations do not destroy underlying magnetic or flash data. Think of it as tearing out a book’s table of contents while leaving every page intact. Standard recovery tools and basic forensic utilities can extract invoices, nondisclosure agreements, executive emails, and client ledgers in minutes.
What Happens Once Assets Leave Your Office?
When disposals are brokered through multi-tiered vendor chains, equipment passes through sub-contractors, third-party logistics hubs, and shared transit depots where theft, loss, and unauthorized component harvesting occur. A state-of-the-art corporate firewall counts for nothing if a single decommissioned endpoint slips away with intact drives.
Retiring corporate-owned hardware must be treated as a critical data destruction operation, not a standard facilities clear-out.
2. Internationally Standardized Overwriting & Unrecoverable Physical Destruction
Every corporate-owned PC entrusted to S&T is processed under rigorous technical protocols.
Globally Certified Multi-Pass Sanitization (Advance License)
Our software-based data sanitization runs on certified technology from Advance, strictly adhering to international standards including NIST SP 800-88 Rev. 1 and DoD 5220.22-M.
This enterprise-grade sanitization writes pseudorandom bit patterns across all addressable storage sectors, rendering subsequent hardware-based or lab-level forensic retrieval impossible. The architecture targets hidden drive sectors, reallocated blocks, and SSD wear-leveling pools, ensuring absolute peace of mind even for modern NVMe solid-state drives.
Upon completion, S&T issues an official Certificate of Data Sanitization referencing each unit’s unique hardware serial number, suitable for internal compliance, ISO audits, and board-level risk reporting.
Unreadable and Damaged Drives: Precision Punching & Physical Destruction
Storage media suffering from read errors, dead controllers, or power failures cannot be sanitized via software alone.
S&T never assumes an unreadable drive is safe. Non-booting and mechanically damaged media are processed through dedicated hydraulic hard drive crunchers that pierce and deform magnetic platters and flash memory dies. This structural deformation makes physical reconstruction technically impossible. Photo-verified destruction audit reports are provided upon request.
3. Treating Client Risk as Our Own
Why does S&T hold data sanitization to such uncompromising standards?
Because we are not a hands-off intermediary. We take legal ownership of purchased assets and prepare them for circular enterprise reuse.
When a refurbished computer enters the secondary market under our name, a single residual byte of client data would destroy not only our client’s standing, but the survival and credibility of S&T itself.
“Our clients’ risk is our risk.”
This shared-stake reality drives our culture. Sanitization at S&T is never treated as thoughtless assembly-line labor. Every single drive is audited under the mindset that our enterprise reputation rests on its complete erasure.
Our specialists verify write logs, check sector verification passes, and reconcile physical hardware serials with system registries, combining automated validation with hands-on human oversight.
4. Zero Outsourcing: Dedicated Fleet Transport & Barcode Item Tracking
Advanced wipe algorithms fail if chain of custody breaks down. S&T’s operating model is built around closed-loop custody and granular traceability.
1. Serialized Barcode Tracking
Upon receipt, every unit receives an internal barcoded asset tag linking its manufacturer, model, serial number, and installed drive specifications. From intake and diagnostics to sanitization, degaussing/punching, and final sign-off, asset progression is tracked step-by-step to eliminate batch mix-ups and missed units.
2. Direct On-Site Pickup via Company Fleet
Public consolidation freight risks mishandling, missed checkpoints, or transit loss. S&T personnel collect hardware directly from corporate facilities using our dedicated company vehicles. From your loading dock directly into our secure facility, assets remain within our closed custody chain.
3. All Operations Managed In-House
S&T does not offload hardware to secondary processors or scrap brokers. Diagnostics, software sanitization, mechanical punching, component segregation, and refurbishment cleaning take place exclusively under our direct roof and supervision.
5. Maximizing Asset Recovery While Eliminating Security Exposure
Enterprises often face a trade-off: spend significant budget on disposal vendors to guarantee destruction, or let internal IT staff burn hours manually wiping retired machines.
S&T resolves this dilemma. Through our enterprise procurement and reuse model, we offset sanitization and logistics overhead against the commercial market value of your retired fleet, turning legacy IT hardware into recovered capital rather than an unrecouped expense.
Your internal IT engineers do not need to spend days running bootable wipe utilities. Hand your decommissioned systems directly to us, and we manage safe extraction, full compliance certification, and asset valuation in a unified process.
(Please note: S&T procures corporate-owned IT assets; leased or rented units subject to third-party title agreements cannot be purchased.)
Inquire for a Consultation or Valuation Estimate
Whether managing an enterprise office migration, an organization-wide laptop replacement cycle, or surplus workstation clearance, we adapt seamlessly to your volume and compliance parameters.
- Looking to verify custom data destruction procedures that match internal security policies?
- Seeking an upfront market valuation on decommissioned corporate hardware?
Reach out to our team today to turn retired IT assets into secure, recovered value.
コメント